
Data, AI, Digital, IT & Cybersecurity
Certified Information Systems Security Professional (CISSP) Preparation
Independent bilingual CISSP preparation across eight domains with worked decisions and separate assessments.
Free
Certified Information Security Manager (CISM) Preparation is a free program on ARPS, the Arab Platform for Professional Studies. Bilingual preparation for the four CISM domains in the ISACA outline current on 22 October 2026. Original cases and questions practice security-management decisions; this is neither ISACA's exam nor its credential.
Important notice: Independent preparation; the platform does not administer the official ISACA exam or award CISM.
Optional certificate fee 50% launch discount
$90 instead of $180
331 AED or 338 SAR
Eight modules and 24 lessons move from governance and strategy through risk, the security program, and incident management. Each lesson explains why a choice works, how to carry it out, and its limits in a professional case, followed by practice and review criteria. Modules map to the current ISACA domains and weights: governance 17%, risk 20%, program 33%, and incidents 30%. Bilingual learning checks, internal assessments, and an original readiness mock are separate from the issuer's official questions and results. ISACA announces a revised outline effective 3 November 2026; the current outline must be checked again for study or delivery after that date.
Exercises produce decision, risk, control and incident records with review criteria and source boundaries. Cases are fictional and country-neutral; actual obligations need organization-specific specialist review.
CISM emphasizes management judgment: who owns the consequence of risk, when a decision changes, and how to know whether a control or incident plan works. Cases start from business objectives and incomplete information, compare plausible professional alternatives, and test assumptions that could reverse a recommendation.
For security practitioners organizing experience in governance, risk, program and incident management before an external exam. It does not promise a job, promotion, or credential eligibility.
Connect business goals to security decisions and establish ownership, authority, and constraints before selecting controls.
Build a strategy linked to business outcomes, then translate frameworks into policy, business cases, and measures.
Define scenarios and analyze exposure, weaknesses, evidence, and uncertainty rather than relying on a bare score.
Compare treatments against appetite and tolerance, separate risk and control ownership, and monitor exceptions.
Identify and classify assets and dependencies, then link policy, standards, procedures, and useful metrics.
Design and test controls and manage workforce behavior and suppliers using service-specific evidence.
Align response, continuity, and recovery; prioritize from impact analysis and exercise classification and escalation.
Investigate, contain, communicate, and recover with reliable evidence, then convert reviews into tested improvements.
Subjects unlock in sequence as you progress.
The current ISACA outline and relevant NIST publications support scope and methods. Examples and questions are original; sources, assumptions and the upcoming outline change are dated and bounded.
Current outline tasks are linked to instruction, applied work, and original questions; the mock is not the ISACA exam or recognized training time.
Professional Certification Preparation programs help learners prepare for a recognized external certification through structured knowledge, review, practice questions, and readiness assessments. Arab Platform for Professional Studies (ARPS) does not administer the certification owner's official exam.
Structured self-paced study aligned to the current external certification scope, with knowledge review, practice questions, readiness checks, and internal mock assessments.
The route includes an internal assessment for Arab Platform for Professional Studies (ARPS) completion eligibility and separate mock/readiness assessments that are not the external official exam.
Assessment attempts: 2 per assessment, 7 days apart
The pass mark is announced before the program is published.
The Arab Platform for Professional Studies (ARPS) credential confirms completion of the preparation program only; the target professional certification requires passing the external issuer's examination under its rules.
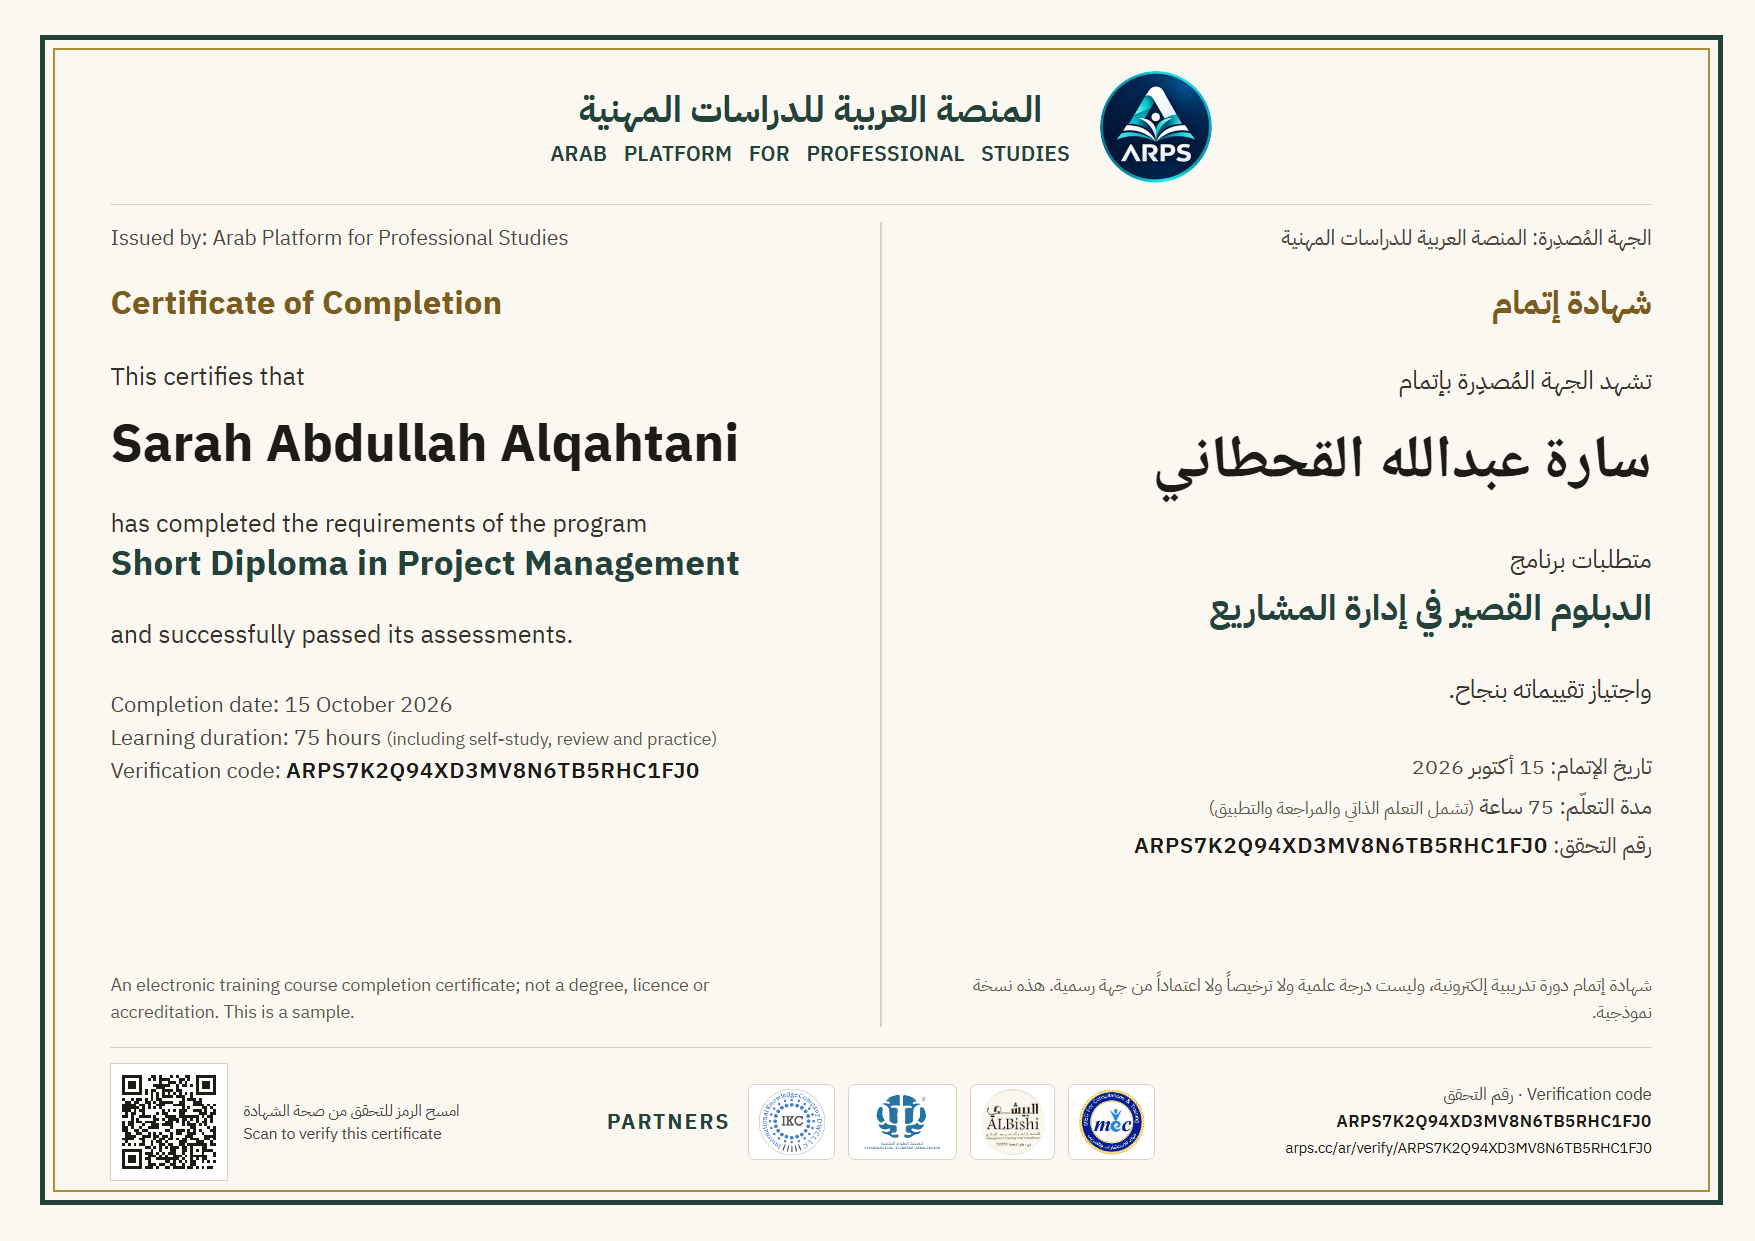
Every certificate has a public verification code. Verify a certificate
The real design with fictional details; opens in a new window.
Verification example: a real issued certificate
Disclaimer: Any internal completion document applies only to this preparation program; it is not CISM or ISACA endorsement.
No. ISACA owns the external certification, requirements, and exam. Any internal completion evidence concerns this preparation program only.
No. They are original educational cases for internal practice and readiness feedback, not official exam items.
The outline displayed by ISACA on 22 October 2026. ISACA says a revised outline takes effect on 3 November 2026, when coverage must be checked again.
No. Minutes are editorial estimates for reading, practice, and one assessment pass; official learning hours are unset pending separate calibration.
No. Internal results guide study and do not determine ISACA eligibility or official exam success.
Yes. Certified Information Security Manager (CISM) Preparation is free on ARPS: every lesson, exercise and assessment is free, the first subject is open to read without an account, and the program is available in Arabic and English. Issuing a certificate is optional; it is a training completion certificate showing you passed the program's assessments, not a university degree, a professional licence or an endorsement by an external body.
The subject of this program is also known as: CISM, Certified Information Security Manager, information security management. Learners usually find it by searching for: CISM exam prep, CISM study guide, CISM practice questions, CISM exam domains, free CISM exam prep, what is CISM certification, CISM exam requirements, CISM course in Arabic.
Programs from the same field or route that may complement what you learn here.
Data, AI, Digital, IT & Cybersecurity
Independent bilingual CISSP preparation across eight domains with worked decisions and separate assessments.
Data, AI, Digital, IT & Cybersecurity
Advanced advisory program on cybersecurity governance, risk scenarios, treatment choices and reviewable executive decisions.
Data, AI, Digital, IT & Cybersecurity
Lead cybersecurity and digital-resilience decisions across risk, identity, incidents, recovery and suppliers through bilingual cases and exercises.
Data, AI, Digital, IT & Cybersecurity
Independent AIGP preparation connects the four domains of the current IAPP blueprint to original bilingual lessons, decision exercises and review questions. Learners study governance, rights, development and monitoring while keeping internal assessment separate from the issuer's official exam.